Identity, not just an IP address
Each employee holds an individual gateway token (stored as a bcrypt hash). Incidents pinpoint the exact identity and tool, never just an anonymous IP.
Security without compromise. XRENN™ EdgeGuardian NIS2 brings cutting-edge AI analysis directly to your network edge – 100% offline, zero data exfiltration, and local policy enforcement. Unique AI Defense 1.0 protection for your audit readiness and NIS2 compliance.
Your team is already using ChatGPT, Claude, and Cursor. Route them through EdgeGuardian. Every prompt is inspected before leaving your premises, every incident is attributed to a specific employee, and the entire engine runs on your local appliance – not in a third-party cloud.
Uses a personal gateway token instead of provider credentials. Only the base_url changes.
The request departs with the corporate provider key, which employees never see.
Each employee holds an individual gateway token (stored as a bcrypt hash). Incidents pinpoint the exact identity and tool, never just an anonymous IP.
Shields against prompt injection, jailbreaks (DAN, AIM, STAN…), system prompt leakage, and exposure of National IDs, VAT numbers, IBANs, and API keys.
An OpenAI-compatible route covers 13 major providers, while Anthropic features a native route. Tools integrate instantaneously without refactoring.
Encrypted provider credentials reside in the appliance hardware vault. Staff never handle production keys. Revoke tokens instantaneously and atomically upon offboarding.
Direct calls to external AI endpoints trigger an ai_gateway_bypass incident. The unit passively
monitors TLS metadata (SNI) without payload decryption.
Incidents from AI Gateway flow directly into PDF audit reports and an accessible REST API for SIEM/SOAR for NIS2 and GDPR auditors.
# Route OpenAI via Gateway (port 8100)
POST /openai/v1/chat/completions
Host: edgeguardian:8100
Authorization: Bearer token_developer
User-Agent: Cursor-IDE (workstation-dev01)

{
  "model": "gpt-4o",
  "prompt": "Analyze source code and sanitize credentials..."
}

# Shadow AI: proprietary source leakage intercepted
# Local pre-flight: secrets, PII, and keys maskedBoth the gateway and AI Defense execute locally on the hardware; prompts never pass through external security clouds. Following inspection, the request safely proceeds to the selected AI provider.
In the unlikely event of detection engine downtime, the gateway never stalls legitimate development or business workflows.
Gateway usage is an organizational policy reinforced by passive SPAN/mirror port bypass detection.
Three straightforward steps to complete NIS2 compliance. XRENN™ EdgeGuardian guides you through initial setup, administrator account creation, and 2FA configuration automatically.
EdgeGuardian connects seamlessly to a mirror port on your core switch. This passive approach guarantees zero operational risk to network stability and zero latency for production traffic.
Within minutes, your "Network Story" comes to life. The system explains in plain language why an endpoint was flagged or why an IoT camera initiated anomalous external traffic, citing relevant NIS2 requirements directly.
Export comprehensive PDF reports tailored for executives and technical auditors alike. Every report is cryptographically authenticated with an HMAC-SHA256 signature, ready for regulatory inspections.
Everything required for end-to-end NIS2 compliance in a unified solution: from real-time telemetry and network topology to policy enforcement and audit reporting.
Edge LLM computation with zero outbound telemetry. Network traffic never leaves your premises. A 100% on-premise engine housing AI models, APIs, and network intelligence locally.
Pioneering detection of confidential corporate data exfiltration to public AI engines. Real-time recognition of weaponized tools like WormGPT, FraudGPT, and prompt injection attacks.
Local gateway for employee AI toolchains: pre-flight prompt inspection, per-user identity instead of shared secrets, and bypass detection. How it works →
Automated generation of audit reports mapped directly to NIS2 requirements. Keep concrete evidence ready for auditors before they ask. Preparedness replaces uncertainty.
Automated discovery of all connected devices with deep OS fingerprinting, CVE mapping, and localized risk scoring.
Continuous detection of traffic anomalies, DNS exfiltration, brute-force attacks, and lateral network movements in real time.
Deploy optional deception containers (RTSP, Telnet, Modbus) across segments to detect reconnaissance and lateral intrusion attempts early.
Automated interactive map depicting network topology and active switches in real time. Gain full visibility into data paths and VLANs without agent installation.
Tamper-proof event recording secured with HMAC-SHA256 (WORM) integrity seals. Satisfies strict non-repudiation mandates for NIS2 and ISO/IEC 27001.
Auditable documentation of technical and organizational security measures under NIS2 (Directive EU 2022/2555). 100% on-premise execution (zero cloud) with GDPR compliance and DPA included. High-performance AI model preventing proprietary data leakage to public AI services.
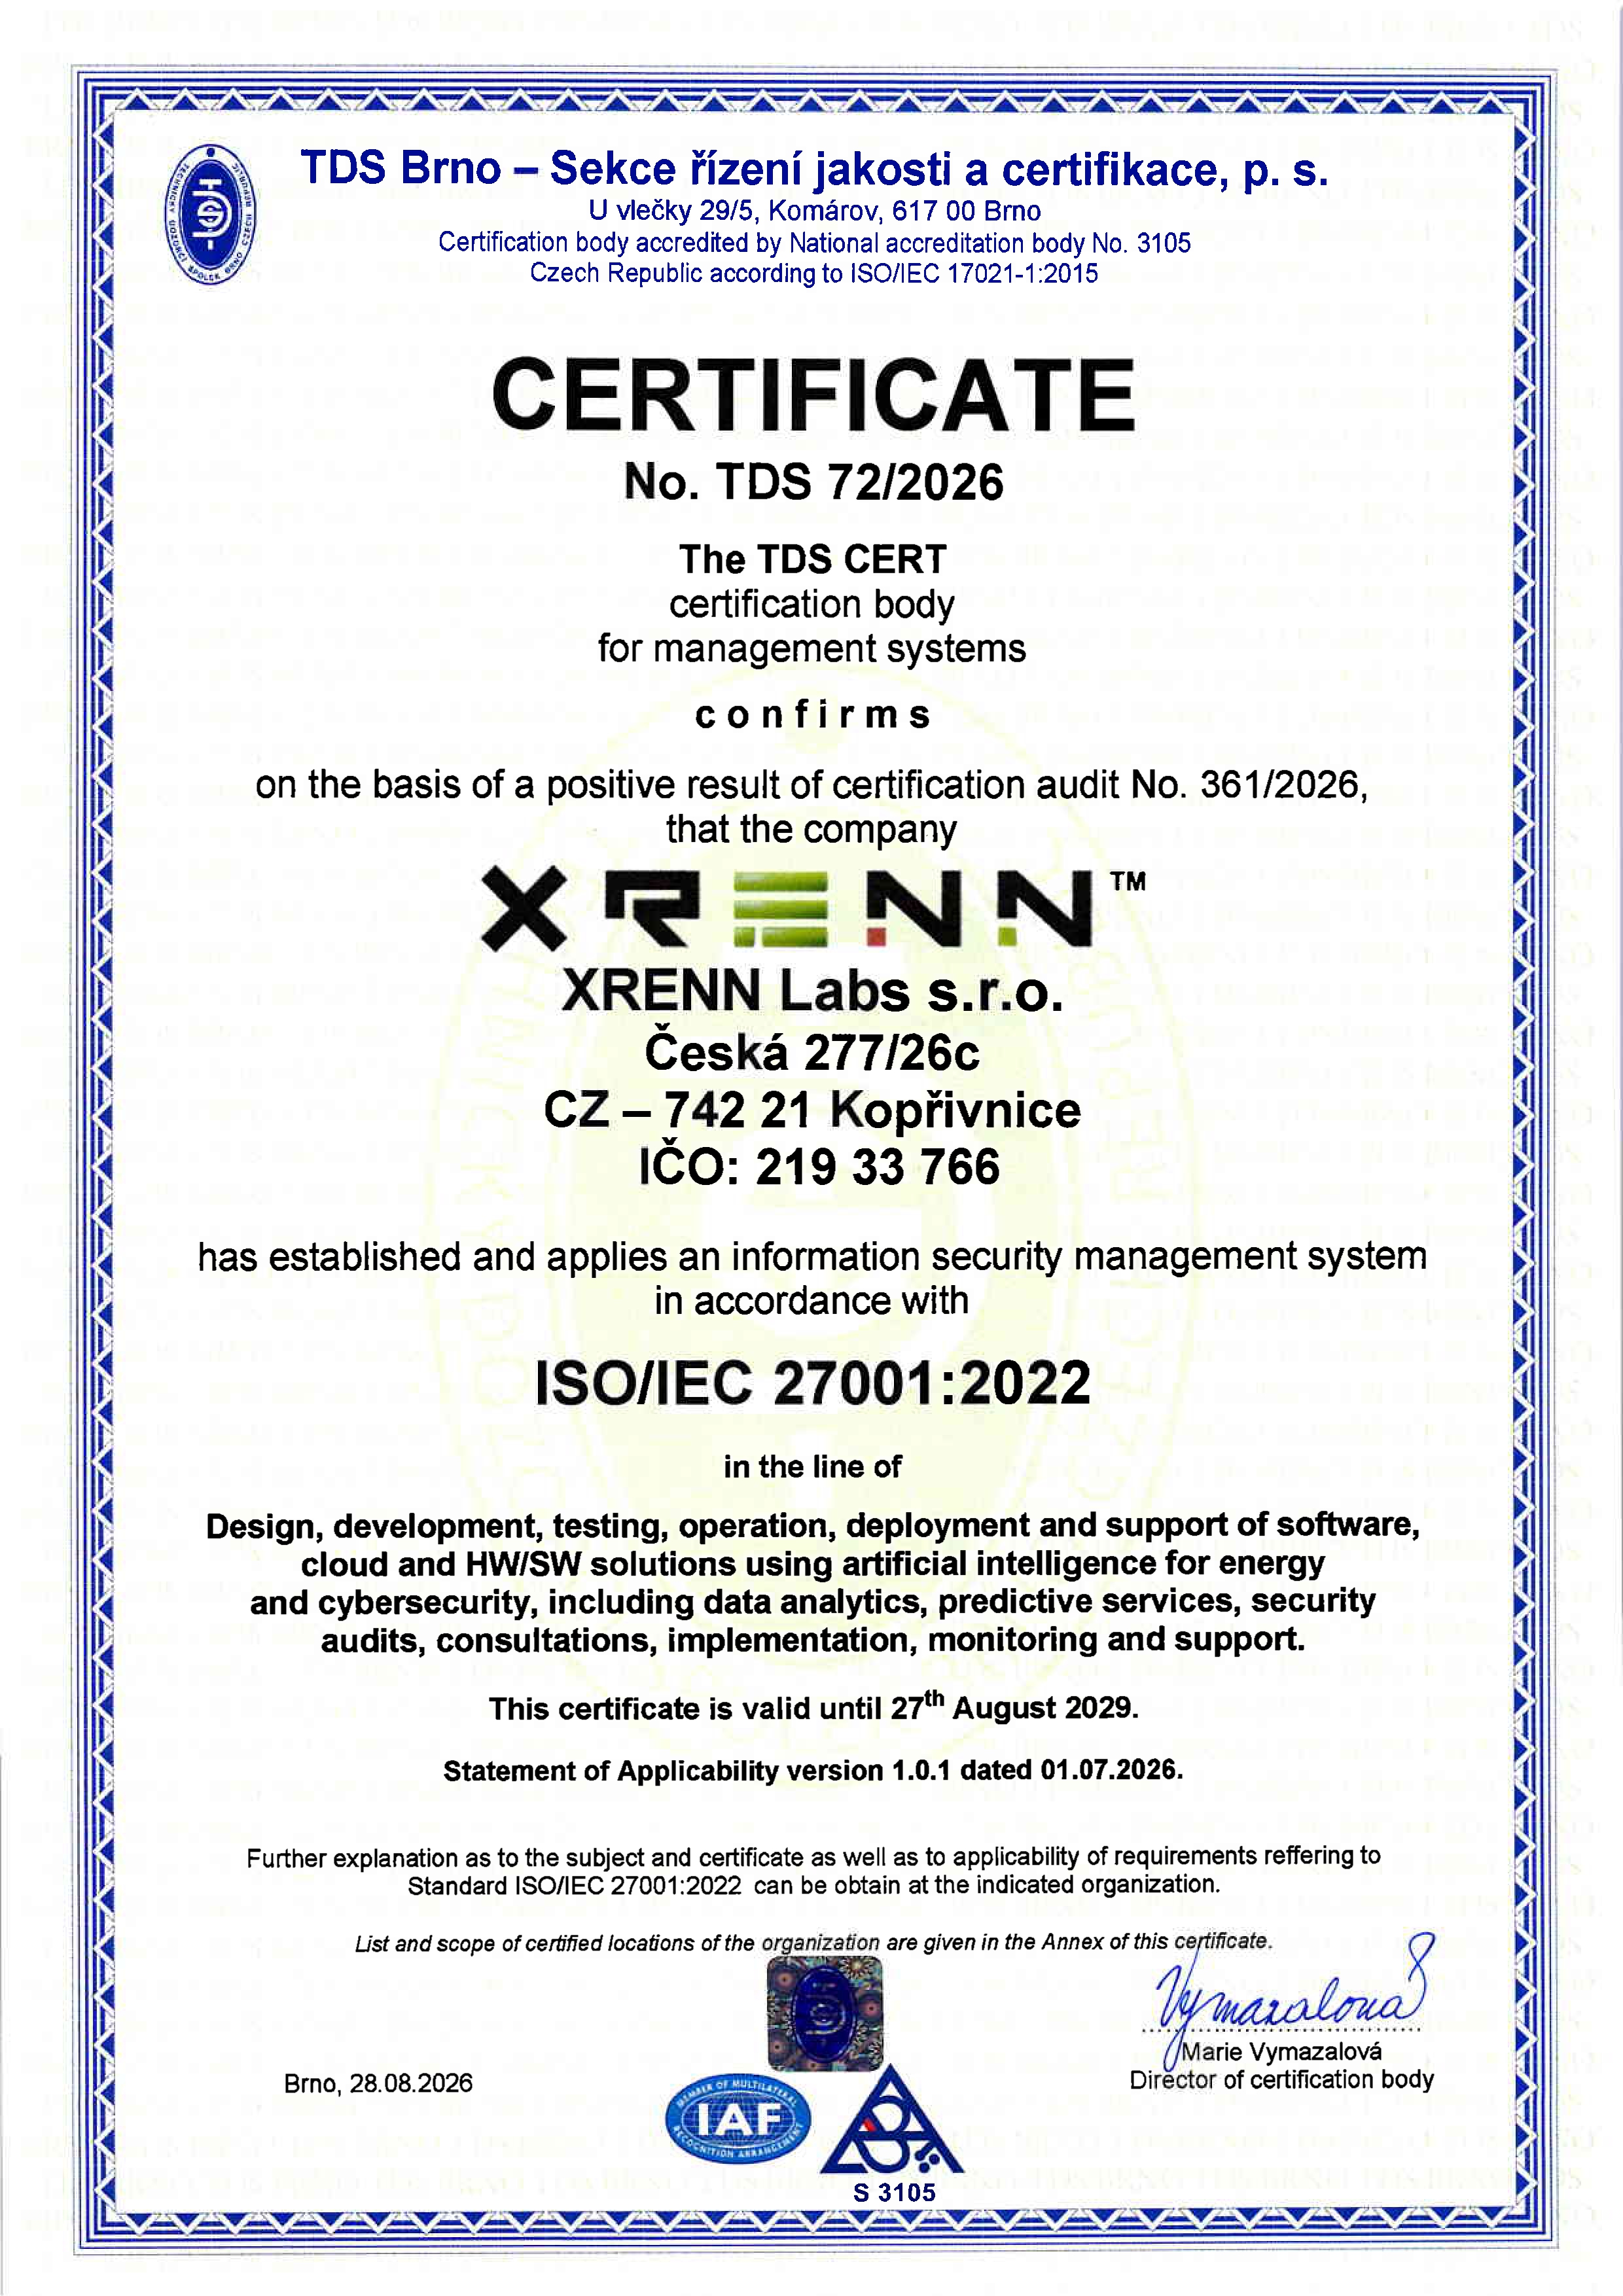
 Corporate Certification
The certificate was awarded by accredited certification body TDS Brno following a rigorous certification audit. The appliance safeguarding your network is developed and maintained by an organization whose own security practices have been verified by an independent accredited authority.
NIS2 mandates thorough supply chain security vetting. Our certified ISMS simplifies vendor risk assessment and procurement compliance.
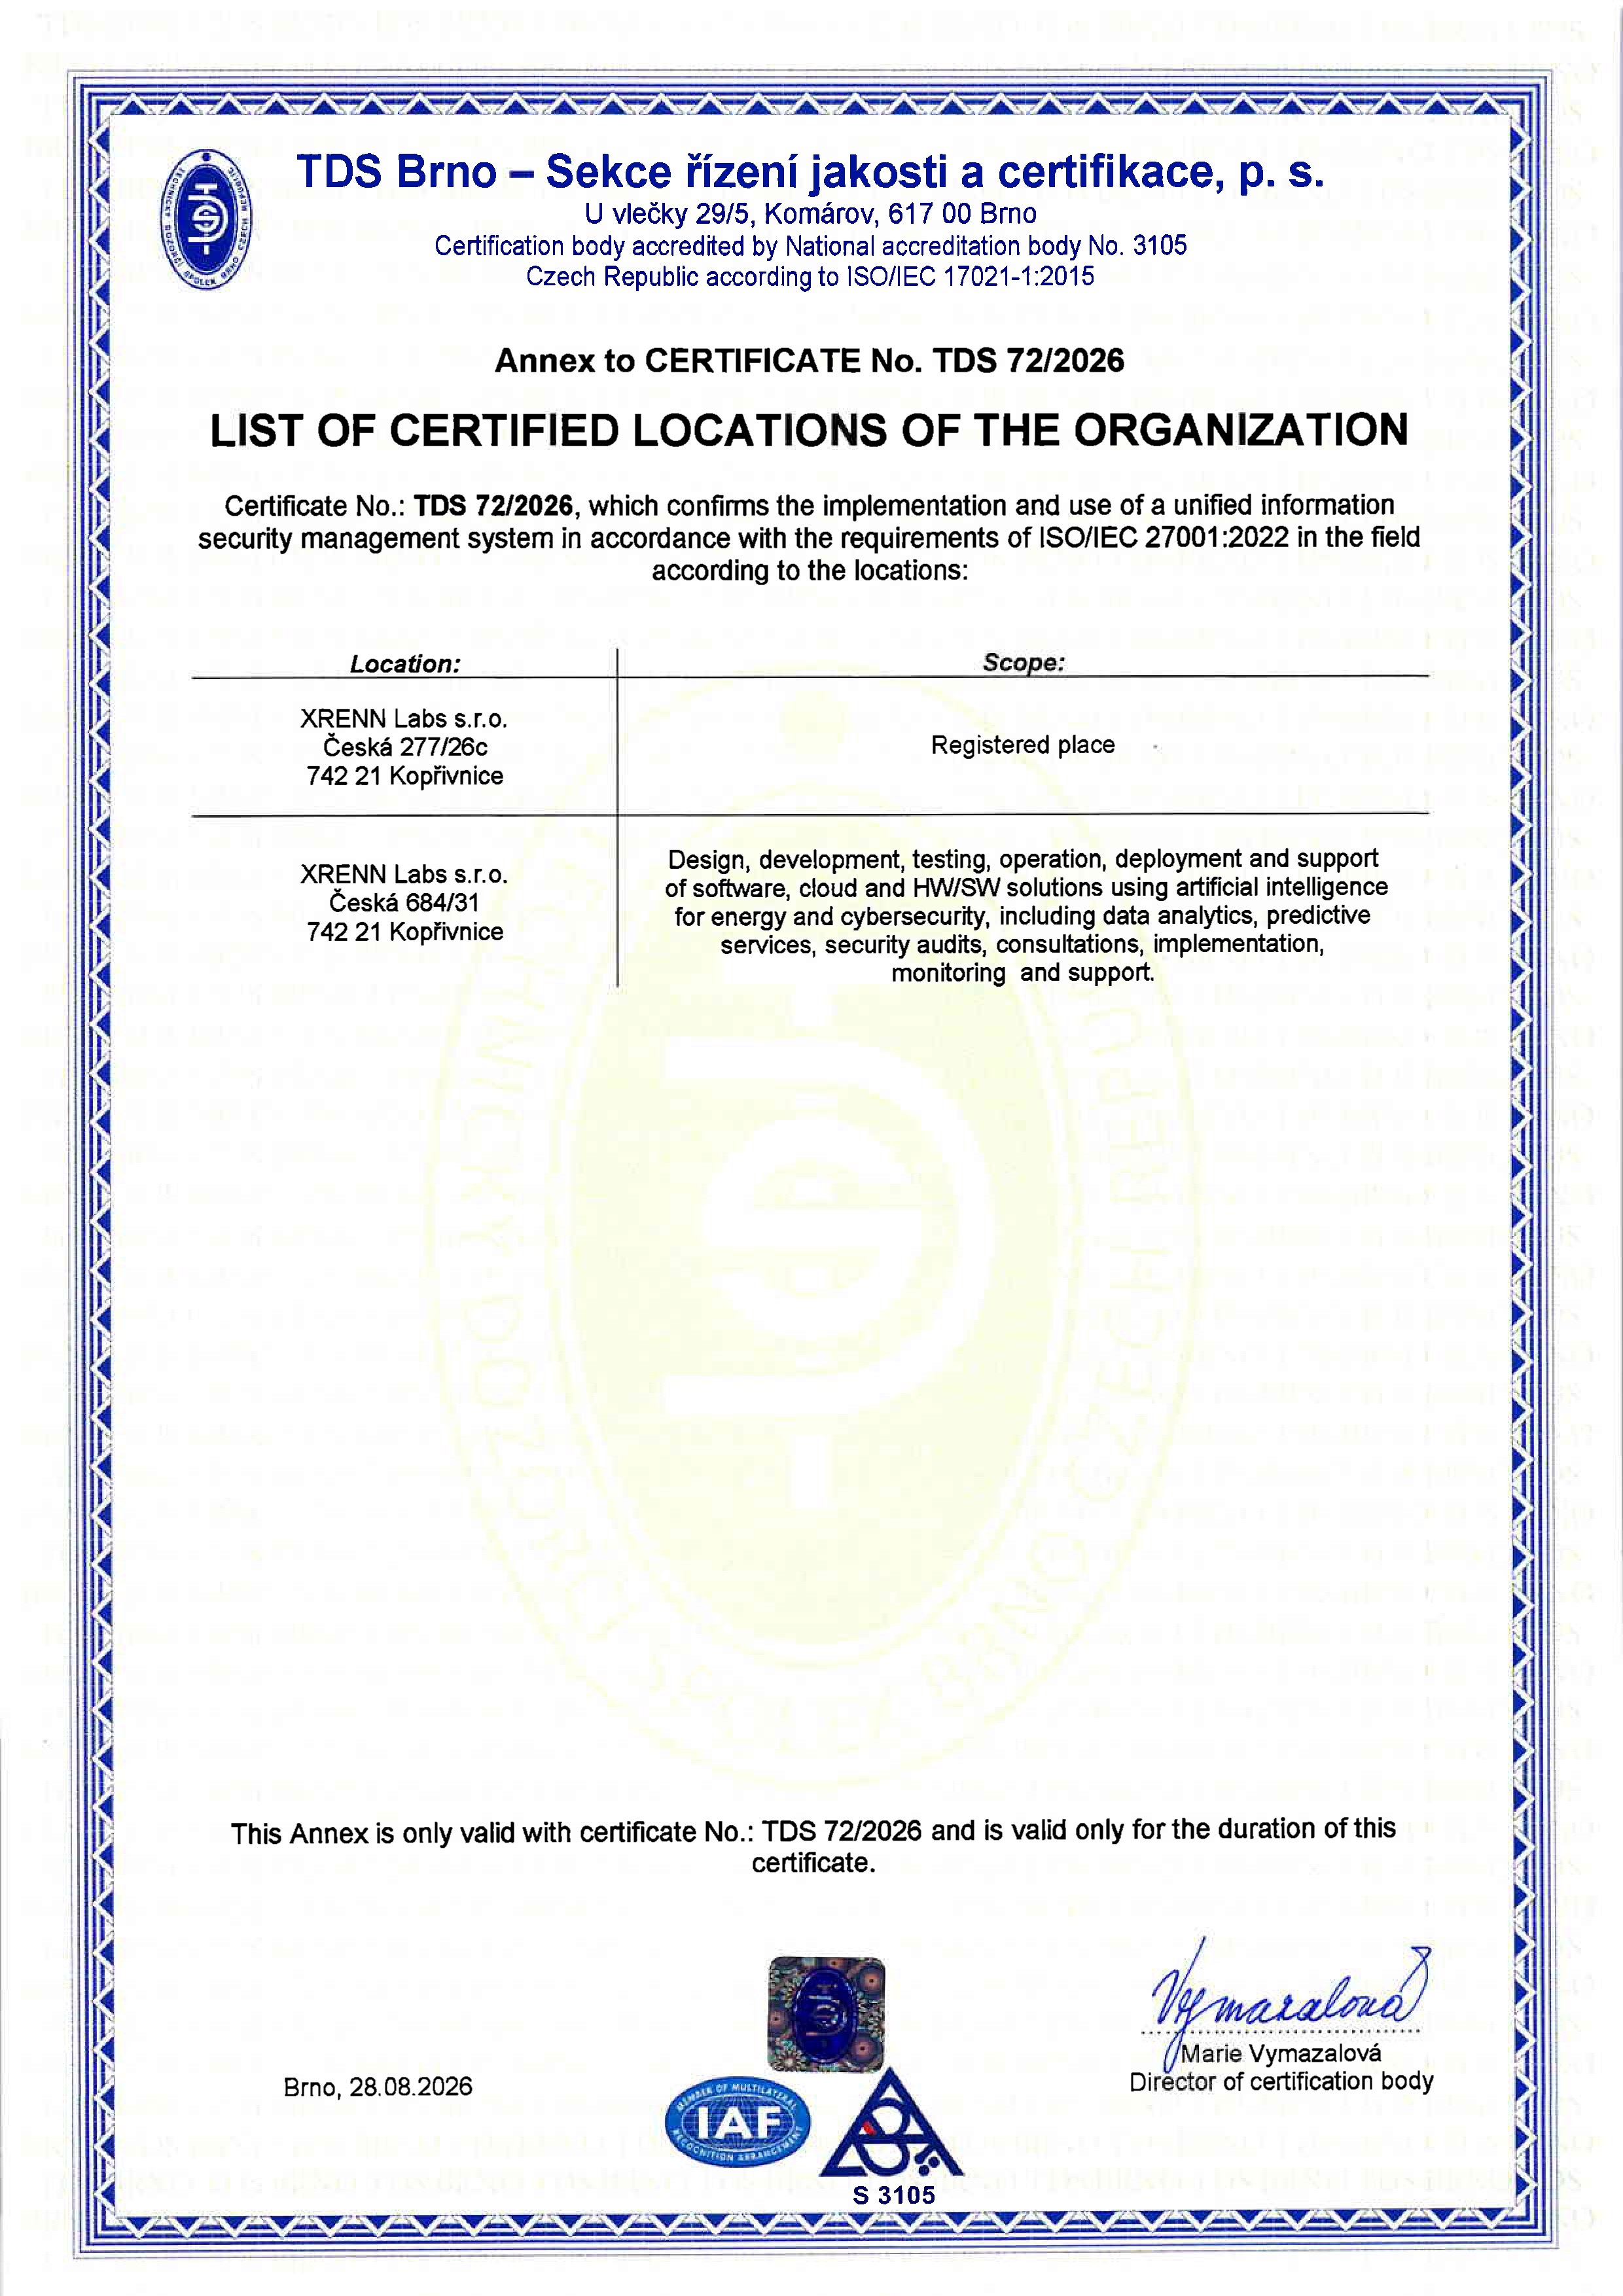
Certification encompasses end-to-end design, development, testing, deployment, and ongoing support for cybersecurity solutions.
Audited by an accredited body under the multilateral IAF MLA framework. Review and download the complete certificate documentation directly.
Your cybersecurity continuity is our utmost priority. We are not merely a hardware supplier – we are your trusted technology partner in sustaining a resilient cybersecurity posture.
Monthly updates for Suricata IDS/IPS signatures and routine OS security patching to eliminate emerging Common Vulnerabilities and Exposures (CVEs).
Continuous alignment of reporting templates and regulatory mapping according to evolving NIS2 guidelines for friction-free compliance audits.
Comprehensive technical guides for the API architecture alongside integration manuals for third-party SIEM/SOAR platforms.
Upgrades to the on-premise Large Language Model (LLM) and ongoing optimization of the RAG knowledge base for refined NIS2 anomaly detection.
In the event of a hardware malfunction, we guarantee immediate dispatch of a replacement unit via Next Business Day (NBD) expedited delivery.
Direct advisory sessions with our L3 cybersecurity engineers for critical incident triage, analysis, and audit response preparation.
Enter the market with an enduring advantage. Safeguard your infrastructure with EdgeGuardian over the long term. Your security begins here.
Geographic expansion into SK, PL, and DE markets. Comprehensive localization for national cyber regulations such as IT-SiG 2.0 and regional NIS2 compliance supported by dedicated local SLAs.
Autonomous behavioral LLM architecture (Zero-Day threat detection), heuristic Deep Packet Inspection (DPI), and automated policy synthesis with formal verification (Z3 solver).
Full inline firewall displacement (Bridge/Gateway) equipped with 2.5GbE/10GbE network interfaces and centralized Zero-Trust Fleet Management spanning multi-site deployments.
Engineered with an open architecture for modern SOC teams. All EdgeGuardian capabilities and telemetry endpoints are accessible via 2FA-secured REST APIs.
XRENN™ EdgeGuardian is not an isolated appliance. Its core is powered by high-performance FastAPI, facilitating sub-millisecond query responses and seamless integration. Built on OpenAPI 3.0.1 standards, it connects directly into existing enterprise SIEM/SOAR pipelines (Swagger/ReDoc).
Predictable, transparent pricing. Guaranteed introductory price of €1,214 excl. VAT until 31 Dec 2026. From 01 Jan 2027, standard retail pricing of €2,055 excl. VAT applies.
The introductory price of €1,214 excl. VAT is firmly locked until 31 December 2026. From 01 January 2027, the standard pricing of €2,055 excl. VAT takes effect. Purchasing today saves you €841, providing full offline hardware and proprietary firmware with a perpetual license and zero recurring fees.
The comprehensive hardware appliance for full NIS2 compliance starts right here!
Everything you need to know about EdgeGuardian NIS2 and network deployment.
No. The device functions in 100% Offline Autonomy mode. All sensitive telemetry is processed locally on your hardware and never leaves your premises. Internet connectivity is strictly optional (opt-in) for remote management (XSC) and instant AI model updates if you choose to enable it.
XSC is an optional secure layer for remote maintenance, signature updates, and RAG knowledge base evolution. Access is granted exclusively through an encrypted SSH tunnel owned by the vendor. You retain absolute control and can enforce Strictly OFFLINE mode at any time.
XRENN's core philosophy is Low TCO. You purchase the hardware and own the software perpetually. Core monitoring and NIS2 compliance capabilities carry zero recurring monthly fees. Optional subscriptions apply only to periodic update packages and expert assistance across BASIC and PRO SLA tiers.
Yes. The appliance is engineered for comprehensive alignment with NIS2 (EU Directive 2022/2555) and associated national cybersecurity laws. It automatically produces audit reports complete with technical summaries and citations of relevant regulatory articles, providing incontrovertible evidence for compliance auditors.
All exported audit reports are cryptographically sealed with an HMAC-SHA256 signature. This guarantees that records have not been altered or tampered with since the moment of generation on the device – fulfilling non-repudiation requirements.
Privacy-by-design is embedded at the architectural foundation. EdgeGuardian automatically masks PII (personally identifiable information such as emails, phone numbers, and credentials) in all outputs and dashboards. With Zero-Cloud execution, no personal records ever transit to third parties.
Deployment is designed to be frictionless. In SPAN/Mirror mode (passive monitoring), the device connects to a mirror port on your network switch. This method has zero impact on throughput, bandwidth, or latency. The system commences asset mapping immediately upon initialization.
2026 is the pivotal enforcement threshold for NIS2 compliance audits across the European Union. Early adoption under the Starter Edition guarantees not only the introductory price discount, but more importantly the runway to compile audit history, fine-tune internal policies, and achieve peace of mind before formal regulatory oversight begins.
Yes. XRENN Labs s.r.o. holds Certificate no. TDS 72/2026 for its Information Security Management System pursuant to ČSN EN ISO/IEC 27001:2023, valid through 27 August 2029. Awarded by TDS Brno (Certification Body no. 3105, accredited by CAI). The certification covers the company's ISMS, verifying organizational security. Download full certificate →
AI Gateway is a dedicated local proxy integrated into the EdgeGuardian appliance. Employees interact with AI services (OpenAI, Anthropic, Mistral, Groq, and others) through this gateway rather than establishing unmanaged external connections. Prior to outbound transit, the gateway intercepts prompts to check for prompt injection, jailbreaks, and leaks of corporate or personal data, attributing incidents to specific users. It delivers oversight and an immutable audit trail for NIS2 and GDPR.
Both the gateway routing layer and the AI Defense security engine run locally on your hardware appliance. Prompt analysis never transits third-party security vendors or XRENN infrastructure. Once inspected and approved, prompts are routed to the specific AI provider designated by the user, identical to standard operation.
Utilizing the gateway is an established corporate policy. To enforce this, EdgeGuardian passively observes
TLS metadata (SNI) on the SPAN/mirror switch port and flags any direct outbound connections to known AI
provider endpoints from non-gateway IPs as an ai_gateway_bypass incident. The unit inspects
transport metadata only – never prompt contents.
Complete audit report ready within 48 hours. Zero commitments. Transparent pricing. 100% OFFLINE.